Open the lab
[ YOUR LAB FILE ]
Download the starting topology, then work through the lesson in SwitchLab.
- Save the .swlab file without renaming its extension.
- Open SwitchLab. Import and export controls currently require a desktop-width window. On a smaller screen, Tools → Fit brings the topology into view.
- Select Import Sandbox (folder icon), choose the downloaded file, and confirm the device and cable counts below.
- Select a device, then choose Open device on desktop or its name in the bottom bar on smaller screens. Select CLI for switches/routers or Desktop → Terminal for PCs. Enter
enableonly when the prompt ends in >. - Follow this page beside the simulator. Use a free account to export your work. Reimport the original download to restart; export any work you want to keep first.
Prerequisites
- Configure router interfaces and read a routing table.
- Understand /24 LANs, a /30 transit subnet, and next-hop addresses.
Topology
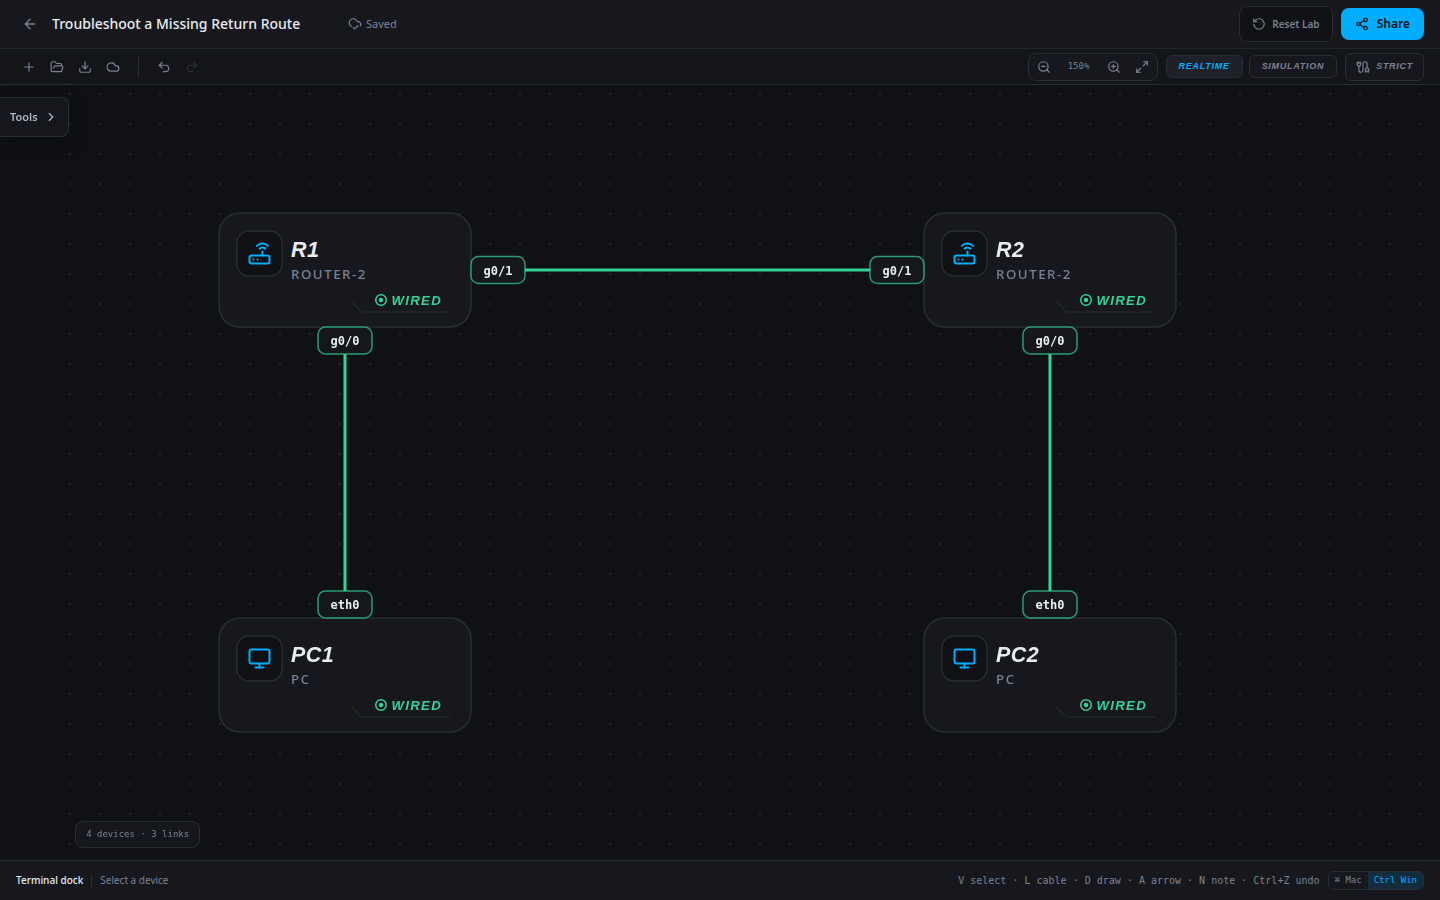
4 devices · 3 links
Scenario
A technician verified the HQ route to the branch and closed a change ticket, but users still cannot communicate. The branch router was replaced and its return route was omitted. Diagnose both halves of the exchange instead of changing the working HQ route.
Objectives
- Inspect the destination lookup at both ends of a failed exchange.
- Identify and restore the missing specific return route.
- Prove both workstation directions while retaining the known-good outbound route.
CCNA blueprint
200-301 v1.1 objectives — this lab covers the following specific skills, not every subtopic in the domain.
- 3.1.a — Identify a static route in the IPv4 routing table.
- 3.1.d — Verify the next-hop address.
- 3.3.b — Configure and verify IPv4 network routes and the return path.
Starting information
- All addresses, local gateways and the transit link are working. R1 already has the approved specific branch /24 route.
- R2 must use a specific 10.10.10.0/24 return route through R1. There is one omitted route and no routing protocol.
- Preserve R1’s route, interface settings and PC gateways; do not substitute a default route for the required specific prefix.
| Host | IPv4 address | Mask | Gateway |
|---|---|---|---|
| PC1 | 10.10.10.10 | 255.255.255.0 | 10.10.10.1 |
| PC2 | 10.20.20.20 | 255.255.255.0 | 10.20.20.1 |
| Router | Interface | IPv4 address | Mask |
|---|---|---|---|
| R1 | g0/0 | 10.10.10.1 | 255.255.255.0 |
| R1 | g0/1 | 10.0.12.1 | 255.255.255.252 |
| R2 | g0/0 | 10.20.20.1 | 255.255.255.0 |
| R2 | g0/1 | 10.0.12.2 | 255.255.255.252 |
| Device / port | Device / port |
|---|---|
| PC1 / eth0 | R1 / g0/0 |
| R1 / g0/1 | R2 / g0/1 |
| PC2 / eth0 | R2 / g0/0 |
Tasks
- Record local gateway tests and failed remote pings. Read R1’s route to PC2’s LAN and explain why it is only part of the evidence.
- On R2 look up the network containing PC1. Compare its connected networks with the required return destination.
- Add only the missing HQ /24 route using the adjacent transit next hop. Keep R1’s configuration intact.
- Verify both remote /24 route entries and both PC directions. Explain the difference between a packet arriving at a destination and a complete successful ping exchange.
Useful commands
show ip interface brief
show ip route
show running-config
ping 10.0.12.2
ip route <network> <mask> <next-hop>
copy running-config startup-config
Progressive hints
Hint 1
Every reply is a new packet that needs its own forwarding decision. Inspect the branch router, even if the HQ table looks correct.
Hint 2
R2 does not have a connected interface in the HQ workstation subnet. It needs a route to that prefix.
Hint 3
Use the specific HQ prefix 10.10.10.0/24 and next hop 10.0.12.1 on R2.
Verification
- R1’s branch route is present before and after repair. Local gateway checks work throughout.
- R2 initially lacks 10.10.10.0/24; afterward it has an S route via 10.0.12.1.
- Both PC directions change from failed to successful.
- No default route or dynamic routing process was added.
Solution / walkthrough
Show Solution
Use enable only from a > prompt; if already at #, begin with configure terminal.
R2
R1 already forwards toward the branch correctly. The missing reciprocal route prevents the exchange from completing; restore that specific route on R2.
enable
configure terminal
ip route 10.10.10.0 255.255.255.0 10.0.12.1
end
copy running-config startup-config
Run every verification check above after the changes. A saved configuration alone does not prove packet delivery.