Open the lab
[ YOUR LAB FILE ]
Download the starting topology, then work through the lesson in SwitchLab.
- Save the .swlab file without renaming its extension.
- Open SwitchLab. Import and export controls currently require a desktop-width window. On a smaller screen, Tools → Fit brings the topology into view.
- Select Import Sandbox (folder icon), choose the downloaded file, and confirm the device and cable counts below.
- Select a device, then choose Open device on desktop or its name in the bottom bar on smaller screens. Select CLI for switches/routers or Desktop → Terminal for PCs. Enter
enableonly when the prompt ends in >. - Follow this page beside the simulator. Use a free account to export your work. Reimport the original download to restart; export any work you want to keep first.
Prerequisites
- Complete VLAN Guided Lab and distinguish VLAN membership from IP addressing.
Topology
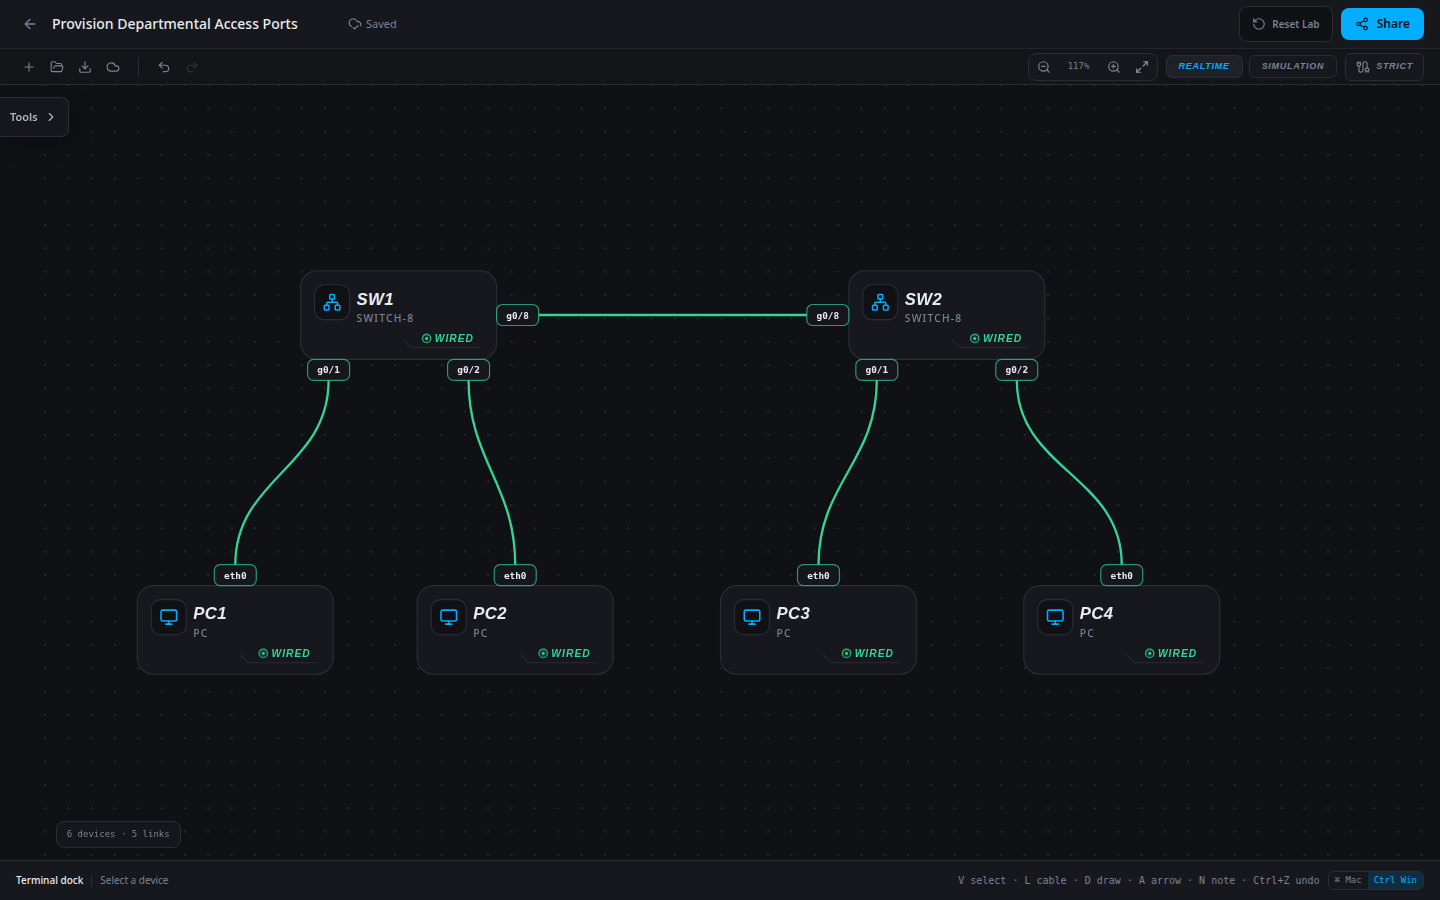
6 devices · 5 links
Scenario
Two closets are connected by a working trunk, but all new workstation ports still use VLAN 1. The restricted uplink carries VLANs 10 and 20, so the new hosts cannot yet reach their peers across it. Your job is to implement the approved department separation.
Objectives
- Translate the approved VLAN plan into switch configuration.
- Verify port membership and every trunk in the path.
- Preserve working traffic while proving the new department or uplink.
CCNA blueprint
200-301 v1.1 objectives — this lab covers the following specific skills, not every subtopic in the domain.
- 2.1.a — Configure data access VLANs.
- 2.2.a — Configure trunk ports and restricted VLAN carriage.
- 2.2.b — Use 802.1Q VLAN separation across switches.
Starting information
- STUDENTS uses VLAN 10 on g0/1 of both switches; STAFF uses VLAN 20 on g0/2. VLAN definitions and the g0/8 trunk already exist.
- Keep all IP addresses and the trunk allowed list unchanged. The trunk deliberately excludes VLAN 1; fix host membership rather than widening the trunk.
| Host | IPv4 address | Mask | Gateway |
|---|---|---|---|
| PC1 | 192.168.10.10 | 255.255.255.0 | None |
| PC2 | 192.168.20.20 | 255.255.255.0 | None |
| PC3 | 192.168.10.30 | 255.255.255.0 | None |
| PC4 | 192.168.20.40 | 255.255.255.0 | None |
| Device / port | Device / port |
|---|---|
| PC1 / eth0 | SW1 / g0/1 |
| PC2 / eth0 | SW1 / g0/2 |
| SW1 / g0/8 | SW2 / g0/8 |
| PC3 / eth0 | SW2 / g0/1 |
| PC4 / eth0 | SW2 / g0/2 |
Tasks
- Inventory both access-port configurations and test both departmental paths before changing anything. Explain why VLAN 1 host traffic cannot cross the restricted uplink.
- Implement the department-to-port plan on both switches, preserving the existing VLAN definitions and uplink policy.
- Prove each port belongs to the approved VLAN with interface configuration output.
- Repeat both directions of student and staff pings, confirm no inter-department gateway exists, and save/export the result.
Useful commands
show vlan brief
show interfaces trunk
show running-config interface g0/1
show running-config interface g0/2
copy running-config startup-config
Progressive hints
Hint 1
Separate VLAN existence, access-port assignment and trunk carriage when diagnosing the path.
Hint 2
Every switch carrying a VLAN needs that VLAN locally, and both ends of every transit link need compatible trunk policy.
Hint 3
Use show running-config interface for the affected port; compare switchport access vlan on host ports and switchport trunk allowed vlan on uplinks against the approved plan.
Verification
- STUDENTS uses VLAN 10 on g0/1 of both switches; STAFF uses VLAN 20 on g0/2. VLAN definitions and the g0/8 trunk already exist.
- Keep all IP addresses and the trunk allowed list unchanged. The trunk deliberately excludes VLAN 1; fix host membership rather than widening the trunk.
- Student and Staff paths succeed in both directions; configuration output matches the required membership and trunk policy.
Solution / walkthrough
Show Solution
Use enable only from a > prompt; if already at #, begin with configure terminal.
SW1
Provision the departmental access memberships; the VLAN definitions and uplink are already correct.
enable
configure terminal
interface g0/1
switchport mode access
switchport access vlan 10
exit
interface g0/2
switchport mode access
switchport access vlan 20
end
copy running-config startup-config
SW2
Provision the departmental access memberships; the VLAN definitions and uplink are already correct.
enable
configure terminal
interface g0/1
switchport mode access
switchport access vlan 10
exit
interface g0/2
switchport mode access
switchport access vlan 20
end
copy running-config startup-config
Run every verification check above after the changes. A saved configuration alone does not prove packet delivery.