Open the lab
[ YOUR LAB FILE ]
Download the starting topology, then work through the lesson in SwitchLab.
- Save the .swlab file without renaming its extension.
- Open SwitchLab. Import and export controls currently require a desktop-width window. On a smaller screen, Tools → Fit brings the topology into view.
- Select Import Sandbox (folder icon), choose the downloaded file, and confirm the device and cable counts below.
- Select a device, then choose Open device on desktop or its name in the bottom bar on smaller screens. Select CLI for switches/routers or Desktop → Terminal for PCs. Enter
enableonly when the prompt ends in >. - Follow this page beside the simulator. Use a free account to export your work. Reimport the original download to restart; export any work you want to keep first.
Prerequisites
- Complete IPv4 routing and standard ACL fundamentals.
Topology
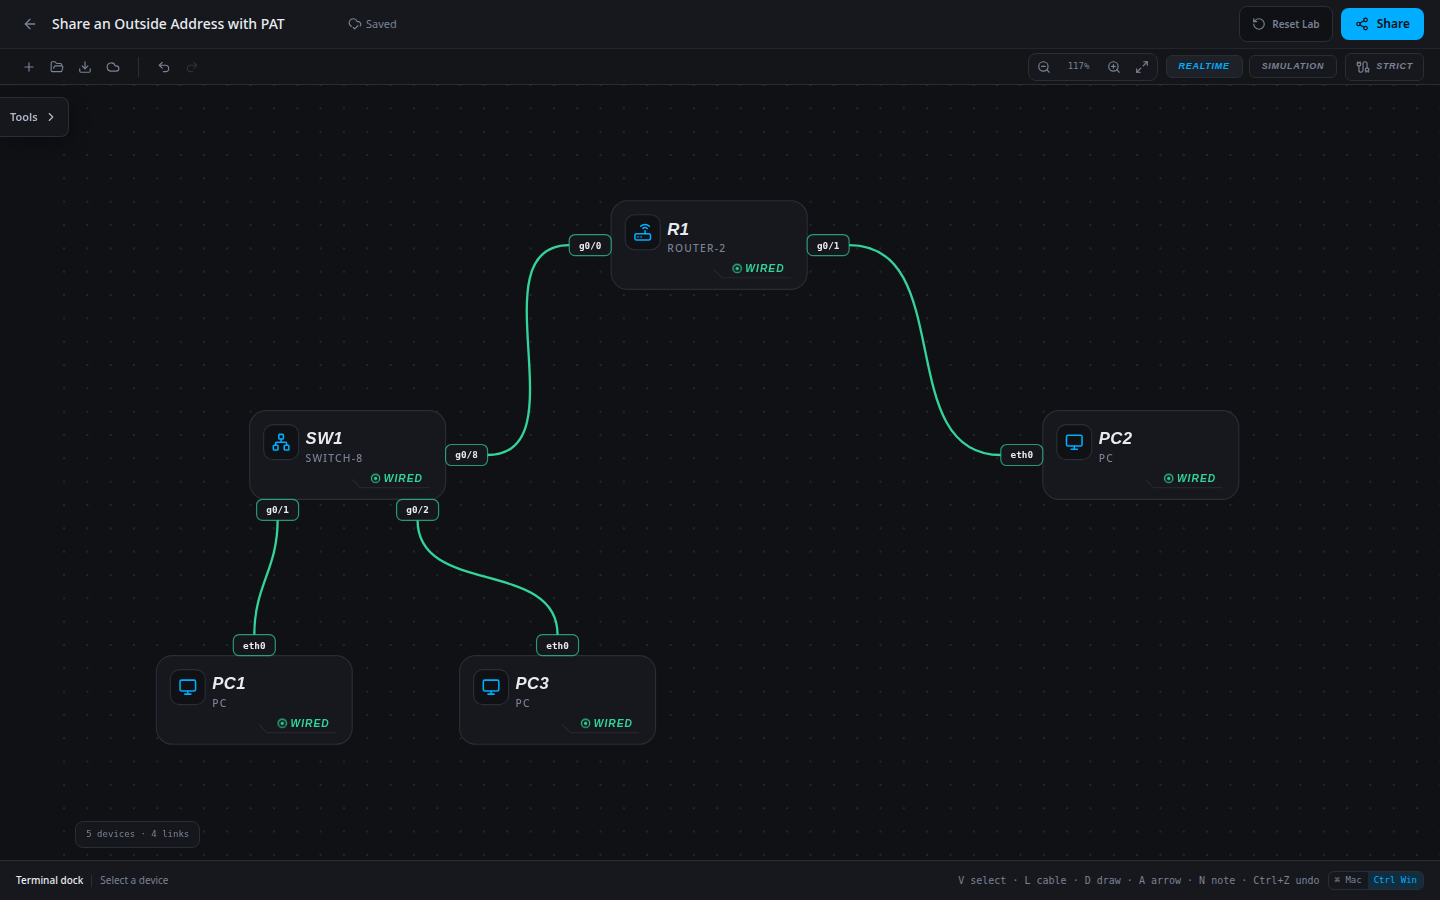
5 devices · 4 links
Scenario
Two private clients need to reach the outside test host through one routable interface address. Configure PAT and verify that both inside hosts receive translations.
Objectives
- Configure the approved NAT rule and interface roles.
- Prove translated delivery and identify local/global addresses in operational evidence.
CCNA blueprint
200-301 v1.1 objectives — this lab covers the following specific skills, not every subtopic in the domain.
- 4.1 — Configure and verify inside-source IPv4 NAT; interface PAT is a related practical extension.
Starting information
- Inside LAN: 10.10.10.0/24 via R1 g0/0=10.10.10.1. Outside: R1 g0/1=203.0.113.1/24 and PC2=203.0.113.20.
- PC2’s configured 203.0.113.254 gateway is intentionally absent; it has no private-LAN return route. Preserve it so untranslated traffic cannot accidentally pass the lab.
- Approved mapping: 10.10.10.0/24 shares R1 g0/1 using ACL 10 and overload.
- Use traffic and translation-table evidence together; NAT configuration text alone does not prove an active translation.
| Host | IPv4 address | Mask | Gateway |
|---|---|---|---|
| PC1 | 10.10.10.10 | 255.255.255.0 | 10.10.10.1 |
| PC3 | 10.10.10.30 | 255.255.255.0 | 10.10.10.1 |
| PC2 | 203.0.113.20 | 255.255.255.0 | 203.0.113.254 |
| Router | Interface | IPv4 address | Mask |
|---|---|---|---|
| R1 | g0/0 | 10.10.10.1 | 255.255.255.0 |
| R1 | g0/1 | 203.0.113.1 | 255.255.255.0 |
| Device / port | Device / port |
|---|---|
| PC1 / eth0 | SW1 / g0/1 |
| PC3 / eth0 | SW1 / g0/2 |
| SW1 / g0/8 | R1 / g0/0 |
| R1 / g0/1 | PC2 / eth0 |
Tasks
- Record baseline inside-to-outside ping failures and inspect the route table, NAT roles and translation configuration.
- Apply the approved mapping and interface roles without giving PC2 a private-LAN return route.
- Generate PC1 traffic to 203.0.113.20, then generate PC3 traffic to the same target.
- Inspect
show ip nat translationsafter the traffic; identify each inside-local address and its approved inside-global address. Save/export and repeat the checks after reload.
Useful commands
show running-config
show ip route
copy running-config startup-config
Progressive hints
Hint 1
Check how the outside host would return a reply to an untranslated private address.
Hint 2
The source ACL selects addresses for translation; it is not applied as a traffic-filtering ACL in this lab.
Hint 3
Mark g0/0 inside and g0/1 outside, then apply the approved static mapping or interface overload rule.
Verification
- Required inside clients reach PC2; the untranslated control stays blocked in the static-NAT lesson.
- Translation output maps the expected inside-local addresses to the approved global address.
- Export/reload retains the configuration and new traffic recreates the required translation behavior.
Solution / walkthrough
Show Solution
Use enable only from a > prompt; if already at #, begin with configure terminal.
R1
Keep inside/outside roles aligned with the physical path and generate real traffic before reading the translation table.
enable
configure terminal
interface g0/0
ip nat inside
exit
interface g0/1
ip nat outside
exit
access-list 10 permit 10.10.10.0 0.0.0.255
ip nat inside source list 10 interface g0/1 overload
end
copy running-config startup-config
Run every verification check above after the changes. A saved configuration alone does not prove packet delivery.